Author: DevenMat Source: X, @DevenMat Translation: Shan Ouba, Jinse Finance
Introducing Agent policies for HyperCore.
Using Hyperliquid as the liquidity backend, individual agents can build a complete financial experience for users on a unified platform. Hyperliquid is positioned as an irreplaceable infrastructure for agents: achieving an ideal balance between deep liquidity, composability, programmability, and trust neutrality.
However, HyperCore lacks the core security capability upon which agents rely—policies.
The so-called strategy refers to defining the scope of permissions: allowing agents to trade only in specific markets, opening positions only after approval, prohibiting agents from transferring funds to unknown addresses, and so on. What enables non-financial personal agents to operate today is precisely this crucial component—scope permissions for your email, calendar, contacts, etc. Modern personal agents rely on cross-platform API access permissions for your account's scope, but Hyperliquid has quietly withdrawn support for it over the past year.
The security of API wallets (formerly known as agent wallets) has deteriorated over time, to the point that Hyperliquid is no longer suitable for granting agents scope access to user accounts.
This article aims to find a path for Hyperliquid to once again become the financial backend for personal agents.
Agent Enters Your Wallet
Personal Agents are the distribution channels, and it is they that make Hyperliquid's vision of "liquidity AWS" the underlying foundation of the daily financial lives of billions of people.
The future of personal finance is Agents that connect to your investment portfolio. Agents act on your behalf—accessing your funds, credentials, and data with permission. For Hyperliquid to become the financial layer for these Agents, account-level permissions are needed: a way to authorize Agents to control access to different parts of an account.
Currently, this can only be achieved through CoreWriter, but the latency makes this architecture incomplete without the native HyperCore control layer.
API wallets must maintain a minimum level of security boundaries to support the user experience required by agents.
Giving an API wallet to an agent today poses a significant and ever-expanding security risk.
Support for agents has been terminated.
The security boundaries initially provided by API wallets (formerly known as agent wallets) have deteriorated over time.
Today, if an account holds approximately $40 million or more in assets, a malicious API wallet could buy 500,000 HYPE tokens, stake them, and then, under the attacker's control, list them on a HIP-3 marketplace. User assets will be locked for 183 days and are subject to slashing. This action is irreversible even if access to the API wallet is subsequently revoked.
This wasn't always the case. Let's review how these boundaries have changed historically.
(The initial boundary) API wallets could not withdraw or transfer funds from accounts.
However, there was never a limit to how much margin an API wallet could use—a compromised API wallet could transfer funds to an attacker by carefully orchestrating bad trades in illiquid markets and having the attacker act as the counterparty.
In 2022, the API keys leaked by the trading bot service 3Commas were used to place unauthorized orders in users' Binance accounts, deliberately targeting the least liquid and most easily manipulated trading pairs.
Besides the aforementioned attack methods, the boundaries of API wallets are constantly expanding into new and unusual exposures not considered in the initial security architecture.
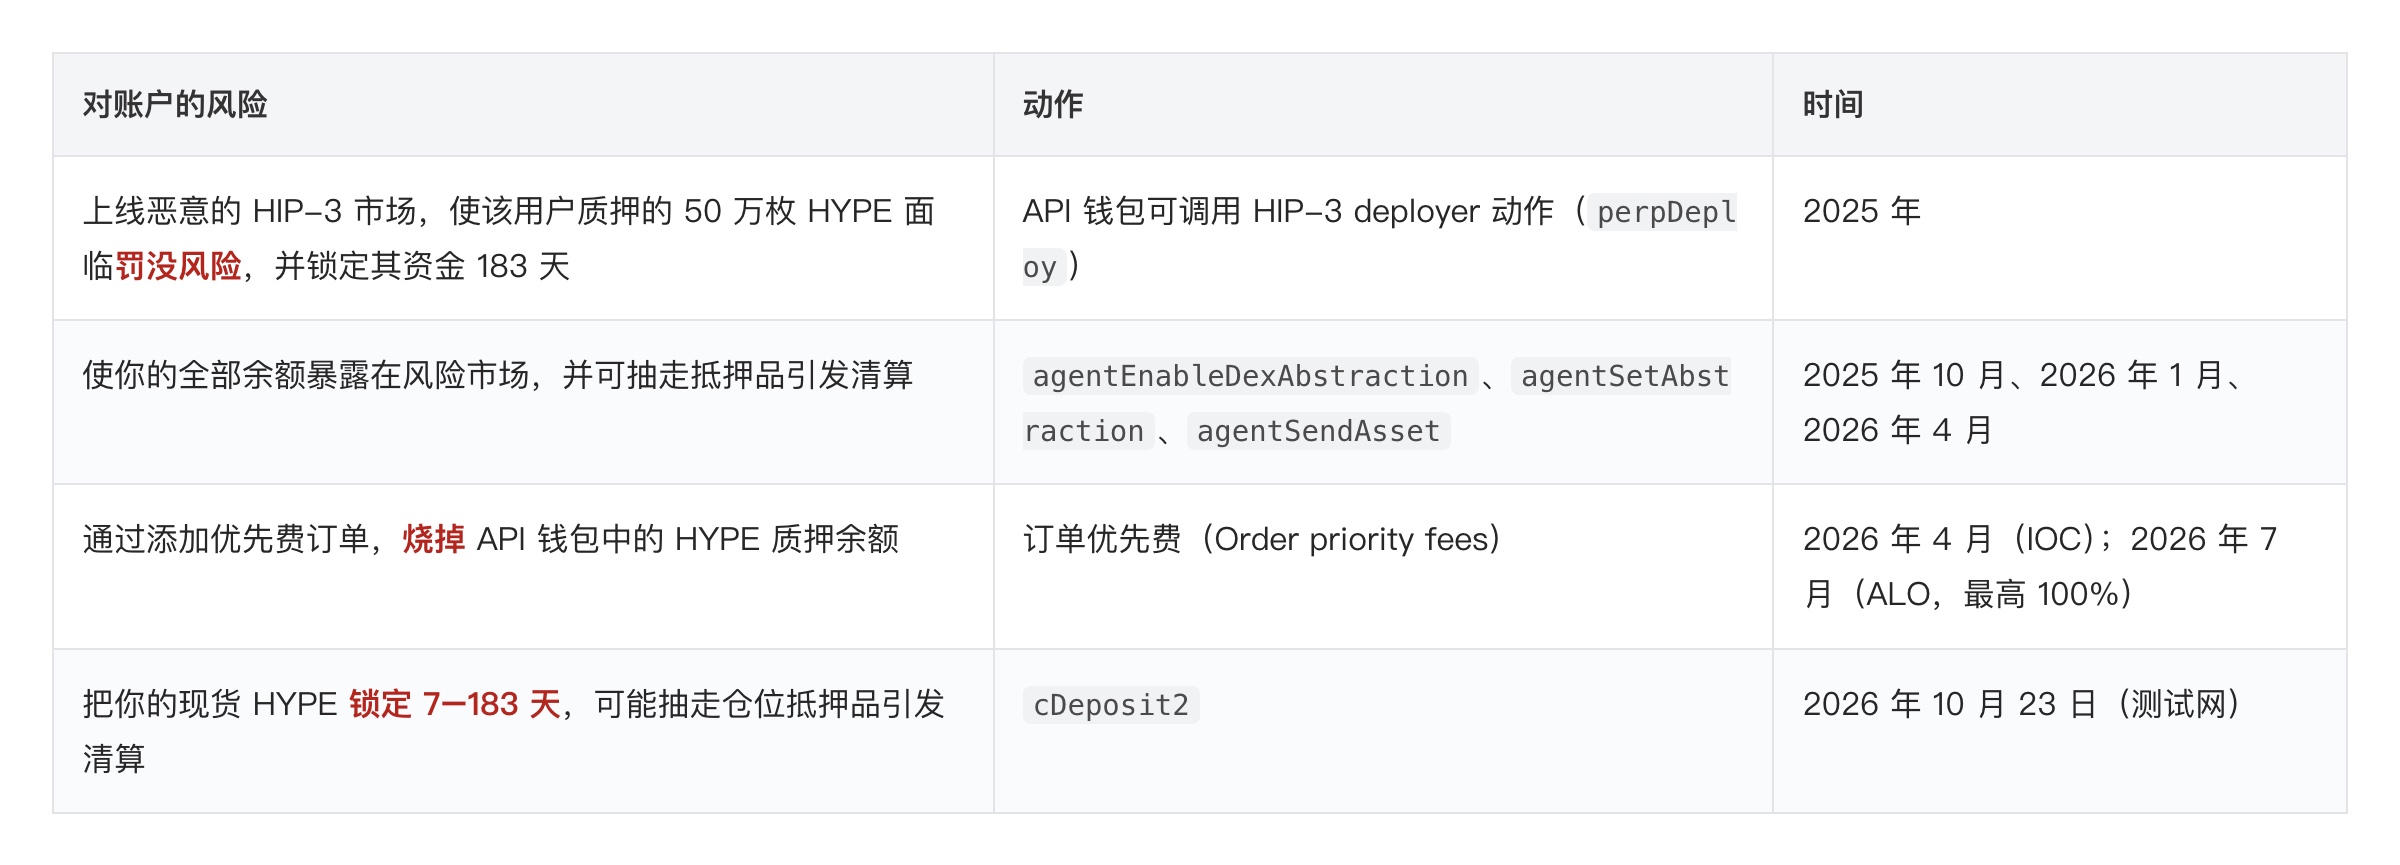
Through a series of unrelated upgrades accumulated during Hyperliquid's long development process, the boundaries of API wallets have become virtually non-existent.
Risk
API wallets have become the default method for users to trade through the Hyperliquid interface. Today, many wallets maintain managed API wallet registrations in multiple builder code applications.
For some trading applications, having dangerous and ever-expanding control over a significant portion of Hyperliquid's user base might be an acceptable risk—but the risk is significantly amplified once an agent is introduced.
An agent doesn't need to reveal your API wallet's private key to empty your account. All it takes is tricking it into reading a piece of malicious text.
Handing over the API wallet to an Agent is equivalent to handing over everything on the list above to anyone who can read it aloud.
Why are API wallet permissions constantly expanding?
Smart contracts on HyperEVM interact with HyperCore through CoreWriter, the framework for programmable applications on Hyperliquid. There are two paths for smart contracts to change the state on HyperCore: CoreWriter actions or the API wallet.
Adding permissions to the API wallet is the easiest way to keep smart contracts and EOA (Entity Access Object) on par. The ideal path is to add a CoreWriter action whenever a latency-insensitive but security-sensitive account primitive appears; however, CoreWriter is a more expensive resource to maintain. In CoreWriter, each action requires its own action ID and node-side support, and is represented as an independent transaction type on HyperCore. Adding actions to the API wallet, however, can simultaneously cover smart contracts and EOAs with minimal resource costs.
Meanwhile, the architecture of all transaction infrastructure on HyperCore is largely the same: a low-latency, locally deployed API wallet hot key, plus an isolated offline cold wallet. Therefore, every latency-sensitive action must reach every API wallet to adapt to the deployment methods of high-value accounts on Hyperliquid. This explains why priority fee expenditures come from the API wallet, and also explains why staking deposits (used to top up priority fee balances) were included in the API wallet's security framework for the first time—likely at the request of priority fee users. The API wallet continues to expand because developers rely on it for various reasons. The problem is that these upgrades invariably increase external applications' control over user accounts, with users having no choice but to join.
Strategies on Hyperliquid
Currently, the best way to implement action-based access control on Hyperliquid is to deploy a smart contract account on HyperEVM, which controls the corresponding address on HyperCore. Each HyperCore action must first undergo a custom Solidity check before being issued through CoreWriter. This is precisely why we built Valantis Prime: it uses Obsidian's CoreWriterLib and a custom Guardian to make HyperCore transactions authoritative and programmable. It can achieve the following:
- HyperCore multisignature with different signers and thresholds for each action.
- HyperCore transfer with whitelist and amount limit.
However, this design completely fails in transaction scenarios.
These transactions must be submitted via HyperEVM, checked by Solidity, and only actually reach HyperCore after the next HyperCore block processes the CoreWriter action. Custom controls are feasible for actions like staking, transfers, and lending; but not for low-latency operations like transactions.
To achieve low latency, direct interaction with HyperCore is necessary using an API wallet, which lacks any constraints or control layer.
Privy provides a managed service that enforces policies before signatures take effect. We anticipate that, given the lack of native primitives to constrain signature permissions at the account level, managed trusted signature middleware will inevitably become a critical dependency for most Hyperliquid users. We believe this is neither desirable nor necessary.
The necessity of relying on trusted middleware to obtain the security primitives necessary for Agents to thrive on Hyperliquid undermines the fundamental reason for Agents to flourish on Hyperliquid—direct connection to a trusted, neutral liquidity infrastructure. When applications need to host private keys on servers, the scope for Agent applications to maneuver shrinks even further. A native policy layer is crucial for Hyperliquid over the next decade.
**Proposal: Add a Permissions field to the API wallet**
**Providing a complete policy layer for the API wallet (including margin limits and market selection) likely violates the HyperCore minimalist architecture. Therefore, we recommend adding a minimal binary permission table at the action level to the API wallet.**
**Implementation can be flexible, but should be as streamlined as possible—for example, using a bitmap to record whether each action type can be called by the API wallet, or adopting an equivalent minimal structure.** Hyperliquid already runs this architecture on the HIP-3 deployer. `setSubDeployers` allows the deployer to grant or revoke the right for another address to invoke a single `perpDeploy` variant on its dex—one authorization per action, set at any time after deployment, and each authorization only covers its corresponding operation.
The same structure applies to API wallets. During a transaction, the signer is recovered, the master account is located, and a bit is checked for the action type to confirm whether the API wallet is authorized to execute the action. The new state is a bitmap for each API wallet.
The core design is that API wallets do not automatically expand permissions due to network upgrades.
Expected Results:
- API scope can be securely expanded. For Agents requiring these permissions, staking, withdrawals, and transfers can all be included in the API wallet scope without sacrificing the overall network security architecture.
- New L1 actions and network upgrades no longer expand the scope of existing API wallets. Adding actions to API wallets is permissible and will not jeopardize the overall network security architecture.
- Accounts on HyperCore become fully programmable, eliminating the need for managed infrastructure—CoreWriter plus a restricted API wallet means that each action can come with custom security settings without causing state bloat on HyperCore.
The power of blockchain lies in its composability and programmability. Hyperliquid made a significant trade-off early on: sacrificing programmability for performance. HyperEVM and CoreWriter were designed to introduce a layer of programmability to HyperCore with minimal resource overhead.
This layer is currently incomplete—it lacks native, minimal API wallet control.
Disclaimer: The assumptions about the Hyperliquid state model in this article are primarily based on testnet transactions. The HyperCore state machine is a black box: node operators run signed binary files, and the code is not publicly available. The overhead of the API wallet carrying strategy can only be estimated based on testnet transactions and publicly visible architectural decisions made by Hyperliquid. Until Hyperliquid releases its node source code, the tools available to the community for making evidence-based change requests remain limited.


 Jasper


